Thursday, November 12, 2026
Home Blog Page 39

States push Medicaid work rules, but few programs help enrollees find jobs : Shots

0

Congress could implement work requirements as part of revamping and downsizing Medicaid.

vm/Getty Images/E+


hide caption

toggle caption

vm/Getty Images/E+

For many years, Eric Wunderlin’s health issues made it hard to find stable employment.

Struggling to manage depression and diabetes, Wunderlin worked part-time, minimum-wage retail jobs around Dayton, Ohio, making so little that he said he sometimes had to choose between paying rent and buying food.

But in 2018, his CareSource Medicaid health plan offered him help getting a job. It connected him to a life coach, who helped him find full-time work with health benefits. Now, he works for a nonprofit social service agency, a job he said has given him enough financial stability to plan a European vacation next year.

“I feel like a real person and I can go do things,” said Wunderlin, 42. “I feel like I pulled myself out of that slump.”

Republicans in Congress and several states, including Ohio, Iowa and Montana, are pushing to implement work requirements for nondisabled adults, arguing that a mandate would encourage enrollees to find jobs. And for Republicans pushing to require Medicaid enrollees to work, Wunderlin’s story could be held up as evidence that government health coverage can help people find employment and, ultimately, reduce their need for public assistance.

Yet his experience is rare. Medicaid typically does not offer such help, and when states do try to help, such efforts are limited.

And opponents point out that most Medicaid recipients already have jobs and say such a mandate would only kick eligible people off Medicaid, rather than improve their economic prospects. Nearly two-thirds of Medicaid enrollees work, with most of the rest acting as caregivers, going to school, or unable to hold a job due to disability or illness, according to KFF, a health information nonprofit that includes KFF Health News.

Existing efforts to help Medicaid recipients get a job have seen limited success because there’s not a lot of “room to move the needle,” said Ben Sommers, a professor of health care economics at the Harvard T.H. Chan School of Public Health. Most Medicaid enrollees already work — just not in jobs with health benefits, he said.

“The ongoing argument that some folks make is that there are a lot of people freeloading in Medicaid,” he said. “That’s just not supported by the evidence.”

Using health care programs to encourage work

The GOP-controlled Congress could allow or require states to implement a Medicaid work requirement as part of revamping and downsizing Medicaid. The first Trump administration encouraged those work mandates, but many were struck down by federal judges who said they were illegal under federal law.

Policy experts and state officials say more attention should be paid to investments that have helped people find better jobs — from personalized life coaching to, in some cases, health plans directly hiring enrollees.

They argue that work requirements alone are not enough. “The move to economic mobility requires a ladder, not a stick,” said Farah Khan, a fellow with the Brookings Institution, a nonpartisan think tank.

While Medicaid work requirements have been debated for decades, the issue has become more heated as 40 states and Washington, D.C., have expanded Medicaid eligibility under the Affordable Care Act to the vast majority of low-income adults. More than 20 million adults have gained coverage as a result — but Republicans are now considering eliminating the billions in extra federal funding that helped states extend eligibility beyond groups including many children, pregnant women and disabled people.

Only Georgia and Arkansas have implemented mandates that some Medicaid enrollees work, volunteer, go to school, or enroll in job training. But a study Sommers co-authored showed no evidence that work requirements in Arkansas’ program led to more people working, in part because most of those who could work already were.

In Arkansas, more than 18,000 people lost coverage under the state’s requirement before the policy was suspended by a federal judge in 2019 after less than a year. Those who lost their Medicaid health care reported being unaware or confused about how to report work hours. Since 2023, Arkansas has been giving Medicaid health plans financial incentives to help enrollees train for jobs, but so far few have taken advantage.

Some plans, including Arkansas Blue Cross and Blue Shield’s, offer members $25 to $65 to complete a “career readiness” certificate. In 2024, some Arkansas health plans offered enrollees educational videos about topics including taxes and cryptocurrency.

Health plans don’t have an incentive to help someone find a better-paying job, because that could mean losing a customer if they then make too much to qualify for Medicaid, said Karin VanZant, a vice president at Clearlink Partners, a health care consulting company.

Rather than offering incentives for providing job training, some states, such as California and Ohio, require the insurance companies that run Medicaid to help enrollees find work.

In Montana, where some lawmakers are pushing to implement work requirements, a promising optional program nearly collapsed after state lawmakers required it be outsourced to private contractors.

Within the program’s first three years, the state paired 32,000 Medicaid enrollees with existing federally funded job training programs. Most had higher wages a year after starting training, the state found.

But enrollment has plummeted to just 11 people, according to the latest data provided by the state’s labor department.

Sarah Swanson, who heads the department, said several of the nonprofit contractors that ran the program shuttered. “There was no real part in this for us to deliver direct services to the folks that walked through our door,” she said. The state hopes to revive job training by allowing the department to work alongside contractors to reach more people.

The hunt for results

State officials say they don’t have much data to track the effectiveness of existing job programs offered by Medicaid plans.

Stephanie O’Grady, a spokesperson for the Ohio Department of Medicaid, said the state does not track outcomes because “the health plans are not employment agencies.”

Officials with CareSource, which operates Medicaid plans in multiple states, say it has about 2,300 Medicaid and ACA marketplace enrollees in its JobConnect program — about 1,400 in Ohio, 500 in Georgia and 400 in Indiana.

The program connects job seekers with a life coach who counsels them on skills such as “showing up on time, dressing the part for interviews, and selling yourself during the interview,” said Jesse Reed, CareSource’s director of life services in Ohio.

Since 2023, about 800 people have found jobs through the program, according to Josh Boynton, a senior vice president at CareSource. The health plan itself has hired 29 Medicaid enrollees into customer service, pharmacy and other positions — nearly all full time with benefits, he said.

In 2022, California started offering nontraditional health benefits through Medicaid — including help finding jobs — for enrollees experiencing homelessness or serious mental illness, or who are otherwise at risk of avoidable emergency room care. As of September, it had served nearly 280,000 enrollees, but the state doesn’t have data on how many became employed.

The University of Pittsburgh Medical Center, which is among the largest private employers in Pennsylvania, running both a sprawling hospital system and a Medicaid plan, has hired over 10,000 of its Medicaid enrollees since 2021 through its training and support services. Among other jobs, they took positions as warehouse workers, customer service representatives and medical assistants.

The vast majority left low-paying jobs for full-time positions with health benefits, said Dan LaVallee, a senior director of UPMC Health Plan’s Center for Social Impact. “Our Pathways to Work program is a model for the nation,” he said.

Josh Archambault, a senior fellow with the conservative Cicero Institute, said Medicaid should focus on improving the financial health of those enrolled.

While the first Trump administration approved Medicaid work requirements in 13 states, the Biden administration or federal judges blocked all except Georgia’s.

“I don’t think states have been given ample chance to experiment and try to figure out what works,” Archambault said.

KFF Health News senior correspondent Angela Hart contributed to this report.

Whistleblower details how DOGE may have taken sensitive NLRB data : NPR

0

The DOGE team may have taken data related to union organizing and labor complaints and hid its tracks, according to a whistleblower.

Charlotte Gomez for NPR


hide caption

toggle caption

Charlotte Gomez for NPR

In the first days of March, a team of advisers from President Trump’s new Department of Government Efficiency initiative arrived at the Southeast Washington, D.C., headquarters of the National Labor Relations Board.

The small, independent federal agency investigates and adjudicates complaints about unfair labor practices. It stores reams of potentially sensitive data, from confidential information about employees who want to form unions to proprietary business information.

The DOGE employees, who are effectively led by White House adviser and billionaire tech CEO Elon Musk, appeared to have their sights set on accessing the NLRB’s internal systems. They’ve said their unit’s overall mission is to review agency data for compliance with the new administration’s policies and to cut costs and maximize efficiency.

But according to an official whistleblower disclosure shared with Congress and other federal overseers that was obtained by NPR, subsequent interviews with the whistleblower and records of internal communications, technical staff members were alarmed about what DOGE engineers did when they were granted access, particularly when those staffers noticed a spike in data leaving the agency. It’s possible that the data included sensitive information on unions, ongoing legal cases and corporate secrets — data that four labor law experts tell NPR should almost never leave the NLRB and that has nothing to do with making the government more efficient or cutting spending.

Meanwhile, according to the disclosure and records of internal communications, members of the DOGE team asked that their activities not be logged on the system and then appeared to try to cover their tracks behind them, turning off monitoring tools and manually deleting records of their access — evasive behavior that several cybersecurity experts interviewed by NPR compared to what criminal or state-sponsored hackers might do.

White House senior adviser Elon Musk walks to the White House after landing in Marine One with President Trump on March 9.

White House senior adviser Elon Musk walks to the White House after landing in Marine One with President Trump on March 9.

Samuel Corum/Getty Images


hide caption

toggle caption

Samuel Corum/Getty Images

The employees grew concerned that the NLRB’s confidential data could be exposed, particularly after they started detecting suspicious log-in attempts from an IP address in Russia, according to the disclosure. Eventually, the disclosure continued, the IT department launched a formal review of what it deemed a serious, ongoing security breach or potentially illegal removal of personally identifiable information. The whistleblower believes that the suspicious activity warrants further investigation by agencies with more resources, like the Cybersecurity and Infrastructure Security Agency or the FBI.

The labor law experts interviewed by NPR fear that if the data gets out, it could be abused, including by private companies with cases before the agency that might get insights into damaging testimony, union leadership, legal strategies and internal data on competitors — Musk’s SpaceX among them. It could also intimidate whistleblowers who might speak up about unfair labor practices, and it could sow distrust in the NLRB’s independence, they said.

The new revelations about DOGE’s activities at the labor agency come from a whistleblower in the IT department of the NLRB, who disclosed his concerns to Congress and the U.S. Office of Special Counsel in a detailed report that was then provided to NPR. Meanwhile, his attempts to raise concerns internally within the NLRB preceded someone “physically taping a threatening note” to his door that included sensitive personal information and overhead photos of him walking his dog that appeared to be taken with a drone, according to a cover letter attached to his disclosure filed by his attorney, Andrew Bakaj of the nonprofit Whistleblower Aid.

The whistleblower’s account is corroborated by internal documentation and was reviewed by 11 technical experts across other government agencies and the private sector. In total, NPR spoke to over 30 sources across the government, the private sector, the labor movement, cybersecurity and law enforcement who spoke to their own concerns about how DOGE and the Trump administration might be handling sensitive data, and the implications for its exposure. Much of the following account comes from the whistleblower’s official disclosure and interviews with NPR.

“I can’t attest to what their end goal was or what they’re doing with the data,” said the whistleblower, Daniel Berulis, in an interview with NPR. “But I can tell you that the bits of the puzzle that I can quantify are scary. … This is a very bad picture we’re looking at.”

The whistleblower’s story sheds further light on how DOGE is operating inside federal systems and comes on the heels of testimony in more than a dozen court cases across the United States that reveal how DOGE rapidly gained access to private financial and personal information on hundreds of millions of Americans. It’s unclear how or whether DOGE is protecting the privacy of that data. Meanwhile, the threatening note, though its origins are unknown, is reflective of the current climate of fear and intimidation toward whistleblowers.

Tim Bearese, the NLRB’s acting press secretary, denied that the agency granted DOGE access to its systems and said DOGE had not requested access to the agency’s systems. Bearese said the agency conducted an investigation after Berulis raised his concerns but “determined that no breach of agency systems occurred.”

Notwithstanding the NLRB’s denial, the whistleblower’s disclosure to Congress and other federal overseers includes forensic data and records of conversations with colleagues that provide evidence of DOGE’s access and activities. Meanwhile, NPR’s extensive reporting makes clear that DOGE’s access to data is a widespread concern. Across the government, 11 sources directly familiar with internal operations in federal agencies and in Congress told NPR that they share Berulis’ concerns, and some have seen other evidence that DOGE is exfiltrating sensitive data for unknown reasons.

A representative of DOGE did not respond to NPR’s requests for comment.

Taking apart computers to protecting government data

Instead of a brand-new car for a 16th-birthday present, Berulis got his first computer.

It’s a familiar story for tech nerds the world over: He methodically took the machine apart “to figure out how it works,” just like he had dissected radios from the thrift store years earlier. “I electrocuted myself once,” he recalled.

Berulis was always interested in public service, but the traditional paths didn’t suit him.

A knee injury prevented him from joining the military. He served as a volunteer firefighter for a period and donated his time working for a local rape crisis hotline, answering calls from victims in need of someone to listen. But, he told NPR, “I had an interest in serving my country.”

Berulis had been a technical consultant for many years, including in auditing and modernizing corporate systems, when a job opened up at the National Labor Relations Board.

Daniel Berulis started working at the National Labor Relations Board about six months before President Trump started his second term.

Daniel Berulis started working at the National Labor Relations Board about six months before President Trump started his second term.

Grace Raver/NPR


hide caption

toggle caption

Grace Raver/NPR

While he didn’t know much about the agency, Berulis quickly found its mission to protect employees’ rights in line with his long-standing desire “to help people.”

He started about six months before President Trump was inaugurated for his second term this past January. Berulis said he hit the ground running, securing the NLRB’s cloud-based data servers and reinforcing what’s called “zero trust” principles, which means that users can get access only to the parts of the system they need in order to do their jobs — no more, no less. That way, if an attacker gets hold of a single username and password, the attacker can’t access the whole system.

“When I first started, it was a dream come true,” he said. “There was a great opportunity to build up and do some good.” But after the inauguration, he described a “culture of fear” descending over the agency.

DOGE arrives 

The first week of March, engineers associated with DOGE arrived at the NLRB’s headquarters, according to Berulis’ disclosure. Beforehand, they had asked about what software, hardware, programming languages and applications the NLRB was using. DOGE learned that it used commercially available cloud infrastructure that businesses typically use, which connects to government cloud systems at other agencies and can be accessed remotely.

Berulis said he and several colleagues saw a black SUV and police escort enter the garage, after which building security let the DOGE staffers in. They interacted with a small number of staffers, never introducing themselves to most of the IT team.

Berulis says he was told by colleagues that DOGE employees demanded the highest level of access, what are called “tenant owner level” accounts inside the independent agency’s computer systems, with essentially unrestricted permission to read, copy and alter data, according to Berulis’ disclosure.

When an IT staffer suggested a streamlined process to activate those accounts in a way that would let their activities be tracked, in accordance with NLRB security policies, the IT staffers were told to stay out of DOGE’s way, the disclosure continues.

For cybersecurity professionals, a failure to log activity is a cardinal sin and contradicts best practices as recommended by the National Institute of Standards and Technology and the Department of Homeland Security’s Cybersecurity and Infrastructure Security Agency, as well as the FBI and the National Security Agency.

“That was a huge red flag,” said Berulis. “That’s something that you just don’t do. It violates every core concept of security and best practice.”

Doge_Spot_01.png

Those forensic digital records are important for record-keeping requirements and they allow for troubleshooting, but they also allow experts to investigate potential breaches, sometimes even tracing the attacker’s path back to the vulnerability that let them inside a network. The records can also help experts see what data might have been removed. Basic logs would likely not be enough to demonstrate the extent of a bad actor’s activities, but it would be a start. There’s no reason for any legitimate user to turn off logging or other security tools, cybersecurity experts say.

“None of this is normal,” said Jake Braun, the executive director of the Cyber Policy Initiative at the University of Chicago’s Harris School of Public Policy and former acting principal deputy national cyber director at the White House, in an interview with NPR about the whistleblower’s disclosure. “This type of activity is why the government buys insider-threat-monitoring technology. So we can know things like this are happening and stop sensitive data exfiltration before it happens,” he told NPR.

However, the NLRB’s budget hasn’t had the money to pay for tools like that for years, Berulis said.

A backdoor to government systems?

A couple of days after DOGE arrived, Berulis saw something else that alarmed him while browsing the internet over the weekend.

Massachusetts Institute of Technology graduate and DOGE engineer Jordan Wick had been sharing information about coding projects he was working on to his public account with GitHub, a website that allows developers to create, store and collaborate on code.

After journalist Roger Sollenberger started posting on X about the account, Berulis noticed something Wick was working on: a project, or repository, titled “NxGenBdoorExtract.”

Wick made it private before Berulis could investigate further, he told NPR. But to Berulis, the title itself was revealing.

“So when I saw this tool, I immediately panicked, just for lack of a better term,” he said. “I kind of had a conniption and said, ‘Whoa, whoa, whoa.'” He immediately alerted his whole team.

While NPR was unable to recover the code for that project, the name itself suggests that Wick could have been designing a backdoor, or “Bdoor,” to extract files from the NLRB’s internal case management system, known as NxGen, according to several cybersecurity experts who reviewed Berulis’ conclusions.

Wick did not respond to NPR’s requests for comment.

A screenshot of DOGE engineer Jordan Wick's public GitHub account that shows "NxGenBdoorExtract." The name itself suggests that Wick could have been designing a backdoor, or "Bdoor," to extract files from the NLRB's internal case management system.

A screenshot of DOGE engineer Jordan Wick’s public GitHub account that shows “NxGenBdoorExtract.” The name itself suggests that Wick could have been designing a backdoor, or “Bdoor,” to extract files from the NLRB’s internal case management system.

Daniel Berulis/Annotation by NPR


hide caption

toggle caption

Daniel Berulis/Annotation by NPR

“It definitely seems rather odd to name it that,” said one of the engineers who built NxGen and asked for anonymity so as not to jeopardize their ability to work with the government again. “Or brazen, if you’re not worried about consequences.”

“The whole idea of removing logging and [getting] tenant-level access is the most disturbing part to me,” the engineer said.

NxGen is an internal system that was designed specifically for the NLRB in-house, according to several of the engineers who created the tool and who all spoke to NPR on condition of anonymity to avoid retaliation or adverse consequences for any future government work.

The engineers explained that while many of the NLRB’s records are eventually made public, the NxGen case management system hosts proprietary data from corporate competitors, personal information about union members or employees voting to join a union, and witness testimony in ongoing cases. Access to that data is protected by numerous federal laws, including the Privacy Act.

Those engineers were also concerned by DOGE staffers’ insistence that their activities not be logged, allowing them to probe the NLRB’s systems and discover information about potential security flaws or vulnerabilities without being detected.

“If he didn’t know the backstory, any [chief information security officer] worth his salt would look at network activity like this and assume it’s a nation-state attack from China or Russia,” said Braun, the former White House cyber official.

Putting the puzzle pieces together

About a week after arriving, the DOGE engineers had left the NLRB and deleted their accounts, according to Berulis’ disclosure to Congress.

In the office, Berulis had had limited visibility into what the DOGE team was up to in real time.

That’s partly because, he said, the NLRB isn’t advanced when it comes to detecting insider threats or potentially malicious actors inside the agency itself. “We as an agency have not evolved to account for those,” he explained. “We were looking for [bad actors] outside,” he said.

But he counted on DOGE leaving at least a few traces of its activity behind, puzzle pieces he could assemble to try to put together a picture of what happened — details he included in his official disclosure.

First, at least one DOGE account was created and later deleted for use in the NLRB’s cloud systems, hosted by Microsoft: “[email protected].”

Then, DOGE engineers installed what’s called a “container,” a kind of opaque virtual computer that can run programs on a machine without revealing its activities to the rest of the network. On its own, that wouldn’t be suspicious, though it did allow the engineers to work invisibly and left no trace of its activities once it was removed.

Then, Berulis started tracking sensitive data leaving the places it’s meant to live, according to his official disclosure. First, he saw a chunk of data exiting the NxGen case management system’s “nucleus,” inside the NLRB system, Berulis explained. Then, he saw a large spike in outbound traffic leaving the network itself.

This screenshot shows a large spike in outbound traffic leaving the NLRB system.

This screenshot shows a large spike in outbound traffic leaving the NLRB system.

Whistleblower Aid


hide caption

toggle caption

Whistleblower Aid

From what he could see, the data leaving, almost all text files, added up to around 10 gigabytes — or the equivalent of a full stack of encyclopedias if someone printed them, he explained. It’s a sizable chunk of the total data in the NLRB system, though the agency itself hosts over 10 terabytes in historical data. It’s unclear which files were copied and removed or whether they were consolidated and compressed, which could mean even more data was exfiltrated. It’s also possible that DOGE ran queries looking for specific files in the NLRB’s system and took only what it was looking for, according to the disclosure.

Regardless, that kind of spike is extremely unusual, Berulis explained, because data almost never directly leaves from the NLRB’s databases. In his disclosure, Berulis shared a screenshot tracking data entering and exiting the system, and there’s only one noticeable spike of data going out. He also confirmed that no one at the NLRB had been saving backup files that week or migrating data for any projects.

Even when external parties like lawyers or overseers like the inspector general are granted guest accounts on the system, it’s only to view the files relevant to their case or investigation, explained labor law experts who worked with or at the NLRB, in interviews with NPR.

“None of that confidential and deliberative information should ever leave the agency,” said Richard Griffin, who was the NLRB general counsel from 2013 to 2017, in an interview with NPR.

“We are under assault right now”

For cybersecurity experts, that spike in data leaving the system is a key indicator of a breach, Berulis explained.

“We are under assault right now,” he remembered thinking.

When Berulis asked his IT colleagues whether they knew why the data was exfiltrated or whether anyone else had been using containers to run code on the system in recent weeks, no one knew anything about it or the other unusual activities on the network, according to his disclosure. In fact, when they looked into the spike, they found that logs that were used to monitor outbound traffic from the system were absent. Some actions taken on the network, including data exfiltration, had no attribution — except to a “deleted account,” he continued. “Nobody knows who deleted the logs or how they could have gone missing,” Berulis said.

The IT team met to discuss insider threats — namely, the DOGE engineers, whose activities it had little insight into or control over. “We had no idea what they did,” he explained. Those conversations are reflected in his official disclosure.

They eventually launched a formal breach investigation, according to the disclosure, and prepared a request for assistance from the Cybersecurity and Infrastructure Security Agency (CISA). However, those efforts were disrupted without an explanation, Berulis said. That was deeply troubling to Berulis, who felt he needed help to try to get to the bottom of what happened and determine what new vulnerabilities might be exploited as a result.

In the days after Berulis and his colleagues prepared a request for CISA’s help investigating the breach, Berulis found a printed letter in an envelope taped to his door, which included threatening language, sensitive personal information and overhead pictures of him walking his dog, according to the cover letter attached to his official disclosure. It’s unclear who sent it, but the letter made specific reference to his decision to report the breach. Law enforcement is investigating the letter.

“If the underlying disclosure wasn’t concerning enough, the targeted, physical intimidation and surveillance of my client is. If this is happening to Mr. Berulis, it is likely happening to others and brings our nation more in line with authoritarian regimes than with open and free democracies,” wrote Bakaj, his attorney, in a statement sent to NPR. “It is time for everyone – and Congress in particular – to acknowledge the facts and stop our democracy, freedom, and liberties from slipping away, something that will take generations to repair.”

In part because of the stymied internal investigation and the attempts to silence him, Berulis decided to come forward publicly.

In fact, despite all that, Berulis managed to uncover some stranger and more troubling details about what happened while DOGE was logged on, which he enumerated in his official declaration.

Unknown users also gave themselves a high-level access key, what’s called a SAS token, meaning “shared access signature,” to access storage accounts, before deleting it. Berulis said there was no way to track what they did with it.

Someone had disabled controls that would prevent insecure or unauthorized mobile devices from logging on to the system without the proper security settings. There was an interface exposed to the public internet, potentially allowing malicious actors access to the NLRB’s systems. Internal alerting and monitoring systems were found to be manually turned off. Multifactor authentication was disabled. And Berulis noticed that an unknown user had exported a “user roster,” a file with contact information for outside lawyers who have worked with the NLRB.

Berulis said he noticed five PowerShell downloads on the system, a task automation program that would allow engineers to run automated commands. There were several code libraries that got his attention — tools that he said appeared to be designed to automate and mask data exfiltration. There was a tool to generate a seemingly endless number of IP addresses called “requests-ip-rotator,” and a commonly used automation tool for web developers called “browserless” — both repositories starred or favorited by Wick, the DOGE engineer, according to an archive of his GitHub account reviewed by NPR.

While investigating the data taken from the agency, Berulis tried to determine its ultimate destination. But whoever had exfiltrated it had disguised its destination too, according to the disclosure.

DOGE staffers had permission to access the system, but removing data is another matter.

Berulis says someone appeared to be doing something called DNS tunneling to prevent the data exfiltration from being detected. He came to that conclusion, outlined in his disclosure, after he saw a traffic spike in DNS requests parallel to the data being exfiltrated, a spike 1,000 times the normal number of requests.

When someone uses this kind of technique, they set up a domain name that pings the target system with questions or queries. But they configure the compromised server so that it answers those DNS queries by sending out packets of data, allowing the attacker to steal information that has been broken down into smaller chunks.

“We’ve seen Russian threat actors do things like this on U.S. government systems,” said one threat intelligence researcher who requested anonymity because they weren’t authorized to speak publicly by their employer. That analyst, who has extensive experience hunting nation-state-sponsored hackers, reviewed the whistleblower’s technical claims.

“The difference is, they were given the keys to the front door,” the researcher continued. While the researcher clarified that it would be difficult to fully verify what happened without full access to the NLRB system, they said Berulis’ conclusions and accompanying evidence were a cause for concern. “None of this is standard,” they said.

Russ Handorf, who served in the FBI for a decade in various cybersecurity roles, also reviewed Berulis’ extensive technical forensic records and analysis and spoke to NPR about his conclusions.

“All of this is alarming,” he said. “If this was a publicly traded company, I would have to report this [breach] to the Securities and Exchange Commission. The timeline of events demonstrates a lack of respect for the institution and for the sensitivity of the data that was exfiltrated. There is no reason to increase the security risk profile by disabling security controls and exposing them, less guarded, to the internet. They didn’t exercise the more prudent standard practice of copying the data to encrypted and local media for escort.”

“Until there’s an investigation done, there’s no way to definitively prove who did it,” Handorf concluded.

“No reason whatsoever for accessing the information”

The National Labor Relations Board seal hangs inside a hearing room at the agency's headquarters in Washington, D.C., in 2019.

The National Labor Relations Board seal hangs inside a hearing room at the agency’s headquarters in Washington, D.C., in 2019.

Andrew Harrer/Bloomberg via Getty Images


hide caption

toggle caption

Andrew Harrer/Bloomberg via Getty Images

DOGE’s intentions with regard to the NLRB data remain unclear. Many of the systems that DOGE embedded itself in across the rest of the government have payment or employment data, information that it could use to evaluate which grants and programs to halt and whom to fire.

But the case management system is very different.

It houses information about ongoing contested labor cases, lists of union activists, internal case notes, personal information from Social Security numbers to home addresses, proprietary corporate data and more information that never gets published openly.

Experts interviewed by NPR acknowledge that there are inefficiencies across government that warrant further review, but they say they don’t see a single legitimate reason that DOGE staffers would need to remove the data from the case management system to resolve those problems.

“There is no reason whatsoever for accessing the information. Now, could any agency be more efficient? More effective? Positively. But what you need for that is people who understand what the agency does. That is not by mining data, putting algorithms in and creating a breach of security,” said Harley Shaiken, a professor emeritus at the University of California, Berkeley who specializes in labor and information technology.

“There is nothing that I can see about what DOGE is doing that follows any of the standard procedures for how you do an audit that has integrity and that’s meaningful and will actually produce results that serve the normal auditing function, which is to look for fraud, waste and abuse,” said Sharon Block, the executive director of Harvard Law School’s Center for Labor and a Just Economy and a former NLRB board member.

“The mismatch between what they’re doing and the established, professional way to do what they say they’re doing … that just kind of gives away the store, that they are not actually about finding more efficient ways for the government to operate,” Block said.

For labor law experts, the mere possibility that sensitive records were copied is a serious danger that could create a chilling effect for employees everywhere who turn to the National Labor Relations Board for protection.

“Just saying that they have access to the data is intimidating,” said Kate Bronfenbrenner, the director of labor education research at Cornell University and co-director of the Worker Empowerment Research Network. “People are going to go, ‘I’m not going to testify before the board because, you know, my employer might get access.'”

Bronfenbrenner, the child of immigrant parents who fled the Soviet Union and Nazi-controlled Germany, said she spends a lot of time thinking about how systems can crumble under the right circumstances. “You know, there’s this belief that we have these checks and balances … but anyone who’s part of the labor movement should know that’s not true,” she told NPR.

With access to the data, it would make it easier for companies to fire employees for union organizing or keep blacklists of organizers — illegal activities under federal labor laws enforced by the NLRB. But “people get fired in this country all the time for the lawful act of trying to organize a union,” said Block.

Having a copy of the opposing counsel’s notes as companies prepare for legal challenges would also be an attractive possibility, she continued.

It’s not just employees who might suffer if this data got out. Companies also sometimes provide detailed statements on internal business planning and corporate structure in the midst of unfair-labor-practice complaint proceedings. If a company was attempting to fire someone who it alleged had disclosed trade secrets and was fighting an unfair-labor-practice complaint based around that decision, those trade secrets might come up in the board’s investigation too. That information would be valuable to competitors, regulators and others.

Overall, the potential exposure of the NLRB’s data could have serious implications.

“I think it is very concerning,” said Shaiken. “It could result in damage to individual workers, to union-organizing campaigns and to unions themselves,” he said.

“It is bringing a wrecking ball into the dentist office, meaning this is wildly disproportionate and raises real dangers,” Shaiken continued.

A conflict of interest and the dangers of exposure

Labor law experts were particularly concerned about what they described as clear conflicts of interest, particularly when it comes to Elon Musk, his companies and his vast network of former employees and allies who are now getting access to government jobs and data.

Trump and Musk, during an interview with Fox News’s Sean Hannity, said Musk would recuse himself from anything involving his companies. “I haven’t asked the president for anything ever,” Musk said. “I’m getting a sort of a daily proctology exam here. You know, it’s not like I’ll be getting away [with] something in the dead of night.” However, DOGE has been granted high-level access to a lot of data that could benefit Musk, and there has been no evidence of a firewall preventing misuse of that data.

There are multiple ongoing cases involving Musk and the NLRB. For one, after a group of former SpaceX employees lodged a complaint with the NLRB, lawyers representing SpaceX, some of whom were recently hired into government jobs, filed suit against the NLRB. They argued that the agency’s structure is unconstitutional.

Elon Musk speaks with then-President-elect Donald Trump and guests at a viewing of the launch of the sixth test flight of the SpaceX Starship rocket on November 19, 2024, in Brownsville, Texas.

Elon Musk speaks with then-President-elect Donald Trump and guests at a viewing of the launch of the sixth test flight of the SpaceX Starship rocket on Nov. 19, 2024, in Brownsville, Texas.

Brandon Bell/Getty Images


hide caption

toggle caption

Brandon Bell/Getty Images

Sen. Chris Murphy, D-Conn. raised his concerns about Musk accessing sensitive labor investigation data on cases against his companies or competitors during the confirmation hearing for Trump’s labor secretary, Lori Chavez-DeRemer, in mid-February. He pressed her to answer whether she believed the NLRB is constitutional and to commit to keeping sensitive data confidential. While she said she was committed to “privacy” and said she respects the NLRB’s “authority,” she insisted that Trump “has the executive power to exercise it as he sees fit.”

All this is happening in the context of a broader attempt by the White House to hamstring labor agencies.

The NLRB was created “to guarantee workers’ rights to organize and to address problems that workers have in the workplace,” said Shaiken, of UC Berkeley. Under President Joe Biden, he recalled, the labor movement enjoyed an unusual amount of support from Washington. “But what we have seen is a sharp slamming of the brakes to that and putting the vehicle in reverse in terms of what Trump has done so far,” he continued.

In addition to sending DOGE to the NLRB, the Trump administration tried to neutralize the board’s power to enforce labor law by removing its member Gwynne Wilcox. Courts have gone back and forth on whether Wilcox’s removal was illegal, as presidents are meant to demonstrate cause for dismissal of independent board members.

Representatives of DOGE and former colleagues of Musk’s who have been installed across the federal government have failed to reassure the public or the courts that they have taken the proper precautions to protect the data they’re ingesting and that private business interests won’t influence how that data is used or what policy decisions are made, Block and the other labor law experts interviewed by NPR say.

“It’s not that he’s a random person who’s getting information that a random person shouldn’t have access to,” said Harvard Law’s Block. “But if they really did get everything, then he has information about the cases the government is building against him,” she said.

“DOGE is, whether they admit it or not, headed by somebody who is the subject of active investigation and prosecution of cases. It is incredibly troubling,” she said.

Musk’s company xAI could also benefit from sucking up all the data DOGE has collected to train its algorithms. Cybersecurity experts like Bruce Schneier, a well-known cryptographer and adjunct lecturer at the Harvard Kennedy School, have pointed to this concern at length in interviews and written pieces.

According to two federal government sources who were not authorized to speak publicly about their workplaces and who shared email documentation with NPR, managers have consistently been warning employees that their data could be subject to AI review, particularly their email responses to the Musk-led campaign to get federal employees to detail “what they did last week” in five bullet points every Monday.

“It’s not a flight of imagination to see several DOGE staffers release some of that [data] surreptitiously to Musk or people close to him,” said Shaiken.

Access for adversaries

Doge_Spot_02.png

If the data isn’t properly protected after it leaves the agency or if DOGE left a digital door open to the agency itself, data could also be exposed to potential sale or theft by criminals or foreign adversaries. An attacker could also try to take advantage of the connections between the NLRB’s cloud account and other government cloud environments, using their access to the NLRB as a foothold to move to other networks.

“Both criminals and foreign adversaries traditionally have used information like this to enrich themselves through a variety of actions,” explained Handorf, the former FBI cyber official. “That includes blackmail, targeting and prioritizing intellectual property theft for espionage or even harming a company to enrich another.”

Within minutes after DOGE accessed the NLRB’s systems, someone with an IP address in Russia started trying to log in, according to Berulis’ disclosure. The attempts were “near real-time,” according to the disclosure. Those attempts were blocked, but they were especially alarming. Whoever was attempting to log in was using one of the newly created DOGE accounts — and the person had the correct username and password, according to Berulis. While it’s possible the user was disguising their location, it’s highly unlikely they’d appear to be coming from Russia if they wanted to avoid suspicion, cybersecurity experts interviewed by NPR explained.

On their own, a few failed login attempts from a Russian IP address aren’t a smoking gun, those cybersecurity experts interviewed by NPR said. But given the overall picture of activity, it’s a concerning sign that foreign adversaries may already be searching for ways into government systems that DOGE engineers may have left exposed.

“When you move fast and break stuff, the opportunity to ride the coattails of authorized access is ridiculously easy to achieve,” said Handorf. What he means is that if DOGE engineers left access points to the network open, it would be very easy for spies or criminals to break in and steal data behind DOGE.

He said he could also see foreign adversaries trying to recruit or pay DOGE team members for access to sensitive data. “It would not surprise me if DOGE is accidentally compromised.”

“This is exactly why we usually architect systems using best practices like the principle of least privilege,” Ann Lewis, the former director of Technology Transformation Services at the General Services Administration, told NPR in an interview. “The principle of least privilege is a fundamental cybersecurity concept … that states that users should have only the minimum rights, roles and permissions required to perform their roles and responsibilities. This protects access to high-value data and critical assets and helps prevent unauthorized access, accidental damage from user errors and malicious actions. “

Bakaj, Berulis’ lawyer, told NPR in a written statement: “This case has been particularly sensitive as it involves the possibility of sophisticated foreign intelligence gaining access to sensitive government systems, which is why we went to the Senate Intelligence Committee directly.”

A troubling pattern

The NLRB isn’t alone in those concerns.

In over a dozen lawsuits in federal courts around the country, judges have demanded that DOGE explain why it needs such expansive access to sensitive data on Americans, from Social Security records to private medical records and tax information. But the Trump administration has been unable to give consistent and clear answers, largely dismissing cybersecurity and privacy concerns.

In one case dealing with Treasury Department payment systems that control trillions of dollars in federal spending, U.S. District Judge Jeannette Vargas blocked DOGE access on Feb. 21, finding “a real possibility exists that sensitive information has already been shared outside of the Treasury Department, in potential violation of federal law.”

It’s an area of focus for Democratic lawmakers on the House Committee on Oversight and Government Reform.

U.S. District Judge Jeannette Vargas blocked DOGE access to the Treasury Department over the possibility that "sensitive information has already been shared outside of the Treasury Department."

U.S. District Judge Jeannette Vargas blocked DOGE access to the Treasury Department over the possibility that “sensitive information has already been shared outside of the Treasury Department.”

Alex Brandon/AP


hide caption

toggle caption

Alex Brandon/AP

An aide for the Democratic minority on the House Oversight Committee who was not authorized to speak publicly told NPR that the committee is in possession of multiple verifiable reports showing that DOGE has exfiltrated sensitive government data across agencies for unknown purposes, revealing that Berulis’ disclosure is not an isolated incident.

But government cybersecurity officials are already resigning or being fired, forced to relocate or put on administrative leave all over the federal government, from the Cybersecurity and Infrastructure Security Agency to the Interior Department. That has limited their power to respond to the ongoing disruptions or keep track of what DOGE is doing.

One of the first people to speak out about DOGE’s access to sensitive data was Erie Meyer, who resigned as the chief technology officer at the Consumer Financial Protection Bureau (CFPB) in February. She has provided testimony in ongoing court cases surrounding DOGE’s access and also spoke to NPR in an interview. The CFPB has sensitive and potentially market-moving data. Meyer said DOGE employees granted themselves “God-tier” access to the CFPB’s systems, turned off auditing and event logs and put the cybersecurity experts responsible for insider threat detection on administrative leave. When IT experts at the CFPB planned to conduct an “after action” report on DOGE’s activities, they were stonewalled, she continued.

When she heard about how DOGE engineers operated at the NLRB, particularly the steps they took to obfuscate their activities, she recognized a pattern.

“I am trembling,” she said upon hearing about the potential exposure of data from the NLRB. “They can get every piece of whistleblower testimony, every report, everything. This is not good.”

Other technical employees working with government agencies who spoke to NPR shared Berulis’ concerns.

“Our cyber teams are pissed because they have to sit on their hands when every single alarm system we have regarding insider threats is going off,” said one employee at an agency of the Interior Department who requested anonymity, fearing retribution. Cybersecurity teams wanted to shut off new users’ access to the system, the employee continued, but were ordered to stand down.

Meanwhile, in a letter published on March 13 on Federal News Network, 46 former senior officials from the General Services Administration, one of the government agencies hardest hit by DOGE’s cost-cutting efforts and that oversees nearly all federal buildings and purchasing, wrote that they believed “highly-sensitive IT systems are being put at risk and sensitive information is being downloaded to unknown, unvetted external sources in clear violation of privacy and data-protection rules.”

The tip of the iceberg

The Trump administration could be trying to codify DOGE’s practices into how the government shares information, said Kel McClanahan, the executive director of nonprofit public interest law firm National Security Counselors, who is representing federal employees in a lawsuit concerning the Office of Personnel Management’s use of a private email server.

Weeks after DOGE staffers descended on federal buildings across Washington, Trump issued an executive order urging increased data sharing “by eliminating information silos” in what’s seen by experts like McClanahan as an attempt to give DOGE engineers further top cover in accessing and amalgamating sensitive federal data, despite laws concerning privacy and cybersecurity.

“The entire reason we have a Privacy Act is that Congress realized 50 years ago that the federal government was just overflowing with information about normal everyday people and needed some guardrails in place,” McClanahan told NPR. “The information silos are there for a reason,” he continued. “It’s astonishing to me that the very people who not a handful of years ago were screaming about the government tracking us with vaccines now cheer for feeding every piece of information about themselves into Elon Musk’s stupid Skynet.”

DOGE appears to still be in the process of visiting federal agencies across the country, including just recently the Securities and Exchange Commission, according to one former government source directly familiar with the matter who requested anonymity to share information they weren’t authorized to share. Across the government, it’s unclear how much sensitive data has been removed and collected and combined.

It’s also unclear where the labor data went and who has access to it. But for experts in workers’ rights, the threat is immediate and existential.

“This shocks the conscience,” said Richard Griffin, the former general counsel of the NLRB. “And if DOGE operatives captured and removed case files, it could constitute a violation of the Privacy Act.”

For Berulis, it was important to speak out, because he believes people deserve to know how the government’s data and computer systems are at risk, and to prevent further damage. As a former IT consultant, Berulis says he would have been fired for operating like DOGE.

Daniel Berulis hopes that there might be further investigations into mishandling of sensitive data across the federal government.

Daniel Berulis hopes that there might be further investigations into mishandling of sensitive data across the federal government.

Grace Raver/NPR


hide caption

toggle caption

Grace Raver/NPR

Disclosing his concerns “was a moral imperative at this point,” he said. “I’ve never encountered this in my 20 years of IT.”

His hope is that there might be further investigations into mishandling of sensitive data across the federal government.

“I believe with all my heart that this goes far beyond just case data,” he said. “I know there are [people] at other agencies who have seen similar behavior. I firmly believe that this is happening maybe even to a greater extent at other agencies.”

For overseers, investigators and IT experts in a similar position, he hopes to provide a road map of what to look for.

“It was my goal by disclosing to Congress not to focus on me at all, but to give them information that they might not necessarily have, the things that you don’t necessarily look for unless you know where to look,” he continued.

The NLRB said it would cooperate with any investigations that stem from Berulis’ disclosure to Congress.

“As an agency protecting employee rights, the NLRB respects its employee’s right to bring whistleblower claims to Congress and the Office of Special Counsel, and the Agency looks forward to working with those entities to resolve the complaints,” said Bearese, the agency’s acting spokesperson, in a statement.

Berulis had a simple request for the DOGE engineers: “Be transparent. If you have nothing to hide, don’t delete logs, don’t be covert. … Be open, because that’s what efficiency is really about. If this is all a huge misunderstanding, then just prove it. Put it out there. That’s all I’m asking.”

But ultimately, if the systems that DOGE accesses are left insecure, it might not matter if its intentions are honorable, he concluded.

“This could just be the start of the operation. … They still haven’t crossed that boundary where they’re plugged into every federal system out there,” he continued. “So maybe there is still time.”

NPR’s Stephen Fowler contributed reporting. NPR’s Brett Neely edited this story. 

Have information or evidence to share about DOGE’s access to data inside the federal government? Reach out to the author, Jenna McLaughlin, through encrypted communications on Signal at jennamclaughlin.54. Stephen Fowler is available on Signal at stphnfwlr.25. Please use a nonwork device.
CDC team cut by DOGE was poised to start a project to help N.C. flood victims : Shots

0

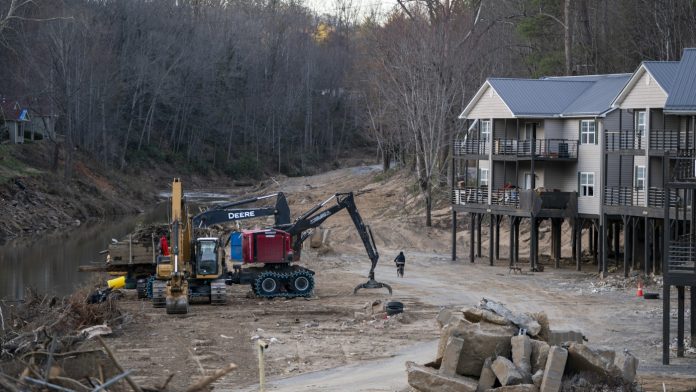
Six months after Hurricane Helene, the landscape of western North Carolina is still scarred. A team of CDC workers was about to go door to door to check on people when they lost their jobs.

Sean Rayford/Getty Images


hide caption

toggle caption

Sean Rayford/Getty Images

In and around Asheville, N.C., there are still visible signs of devastation that remain from the floods of Hurricane Helene six months ago: rusted debris in the yards of water-damaged residences in ruins.

But Helene, a federal disaster worker who coincidentally goes by the same name as the storm, also worries about this community’s invisible problems that tend to persist, months later — like mold and financial and mental health aftereffects.

“That six-month mark is a really critical time,” says Helene, who spoke to NPR on the condition of partial anonymity because she fears retaliation for talking to the media.

Until April 1, Helene worked at the National Center for Environmental Health at the Centers for Disease Control and Prevention. Her team parachutes in after storms, wildfires, factory explosions, or toxic spills to help state and local officials assess where to put emergency resources. Helene and her CDC colleagues lost their jobs in Elon Musk’s DOGE-directed layoffs of about 10,000 staff at federal health agencies.

On April 1, Helene and about 55 other public health workers from the county and state government, as well as a local university, were set to go door to door, surveying 210 households about any enduring challenges facing residents of Asheville’s Buncombe County.

They’d prepared detailed questionnaires about food insecurity, unsafe drinking water and toxic chemical exposure. The mission of Helene’s CDC team was to collect and process that survey data and write up a report — all within 48 hours — so that local officials could solve residents’ most pressing problems.

“The hardest phone calls”

Helene and other CDC colleagues were en route, or already on site in North Carolina, when they all received the “reduction-in-force” emails placing them on administrative leave. They had to abort the mission, and Helene had to deliver the news to their partners at the state and county level.

“It was really one of the hardest phone calls I’ve ever had to do in my career,” says Helene.

The suspended Buncombe County survey is just one example of the many local and state efforts supported by federal health agencies caught up in the Trump administration’s deep cuts to government staffing and spending.

Helene says she feels heartbroken. “I feel like I let down the community; I let down the health department; I let down North Carolina itself,” she says. “I lost my job, but people have lost so much to these disasters and we’re not out there … finding out what the community itself needed.”

Federal cost-cutting rationale

The CDC is part of the federal Department of Health and Human Services. Neither CDC nor HHS responded to requests for comment on the specifics of this story.

In a fact sheet, HHS said CDC’s workforce was being reduced by 2,400 people, and that the goal is to streamline divisions within the agency and get rid of redundancies.

On X, HHS Secretary Robert F. Kennedy Jr. expressed sympathy for those who lost their jobs. “But the reality is clear: what we’ve been doing isn’t working. Despite spending $1.9 trillion in annual costs, Americans are getting sicker every year,” Kennedy wrote in a post. “We must shift course. HHS needs to be recalibrated to emphasize prevention, not just sick care.”

Overall, the HHS workforce is going from approximately 82,000 people to 62,000 people, the agency says, including staff who took offers of early retirement or DOGE’s “fork in the road” offer. Overall, it’s a reduction of 25% of the workforce. HHS is also cutting its contract spending by 35% across the board.

“Human-to-human interaction”

The impact of the cuts on the North Carolina project were immediate. But Helene — and others involved — wonder how the downsizing will affect both federal and local responses to any future disasters.

“I was really, really disappointed,” says Ellis Matheson, Buncombe County’s public health director, who was on the receiving end of one of Helene’s phone calls April 1.

“We had publicized this to the community; they knew that we were going to be coming,” Matheson says. That, too, had to be undone: “We had to notify the public that we would not be coming.”

Matheson says it was a missed opportunity to address people’s needs. “There would have been human-to-human interaction, and people could ask questions, say what resources they need,” she says. “And right there in the moment, we could connect them with those resources.”

Matheson says the county health department plans to eventually regroup, but without the CDC’s help, her team could not carry out the project as planned. “That expertise of being able to help us with the analysis and develop a report was really vital; that subject matter expertise, we really rely on that,” she says.

Devastating storms brought tornado damage and floods to a wide area in the South and Midwest the day after the CDC cut its team that responds to such disasters.

States rely on CDC expertise

Subject matter expertise at the federal level exists at the CDC precisely because it simply isn’t possible or feasible for every state and locality to have its own disaster experts, says Dr. Zack Moore, an epidemiologist with North Carolina’s Department of Health and Human Services. “That’s the reason the CDC exists.”

Moore says the Buncombe County survey is just one example of the ways states routinely rely on the CDC to keep residents safe from disease and disaster. “Beyond hurricanes, they do radiation preparedness, toxicology issues, surveillance for illnesses in Red Cross shelters after a disaster — anything from disease outbreaks to mental health needs,” he says.

As in all other states, Moore says, North Carolina’s health department is also extremely reliant on funding from the CDC — something that’s also been slashed amid Trump’s cuts to federal agencies. Moore, who oversees departments in infectious disease, vaccination and environmental disaster, says 90% of his budget comes from the CDC. Yet he says many people aren’t aware how heavily states rely on federal funding for essential services like his: “We get very little funding from the state.”

There are many worrying public health issues right now, Moore muses — “oh, gosh, hurricanes, measles, flu” — but one of the most pressing new concerns overarching all of them is the hollowing out of the CDC’s environmental health division.

“Having them instantly disbanded is going to leave a big gap,” Moore added.

Ryan Routh, accused of trying to kill Trump, to appear in court : NPR

0

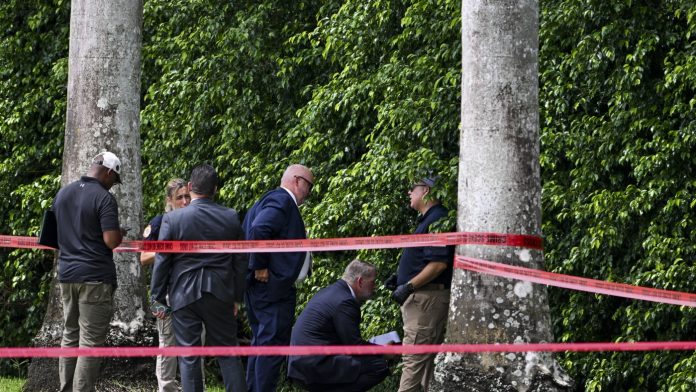
Law enforcement officials work at the crime scene outside the Trump International Golf Club in West Palm Beach, Fla., on September 16, 2024, following the attempted assassination on then-Republican presidential candidate Donald Trump. Ryan Routh is charged in the case and has a federal court hearing on Tuesday in Fort Pierce, Fla.

Chandan Khanna/AFP via Getty Images


hide caption

toggle caption

Chandan Khanna/AFP via Getty Images

FORT PIERCE, Fla. — The man charged with attempting to assassinate Donald Trump when he was running for President last year will be in court Tuesday.

Prosecutors say a Secret Service agent spotted Ryan Routh holding a rifle and fired on him while Trump was golfing at his West Palm Beach club in September.

Routh faces five federal charges. The hearing will focus on the semi-automatic, SKS-style rifle authorities say Routh planned to use in the assassination attempt. Law enforcement authorities found the rifle in what they described as a “sniper’s nest” near the fence just outside of Trump’s golf club. Routh has pleaded not guilty.

The federal agent who was part of Trump’s security detail says he saw a gun barrel poking out from the tree line a few holes ahead of where the then-Presidential candidate was golfing. The agent fired at the person holding the gun. A man, later identified as Routh, fled the scene and was arrested a short time later driving north on Interstate 95.

Routh’s federal public defenders are asking U.S. District Judge Aileen Cannon to give them access to the rifle. They want a defense expert to examine and test-fire the weapon. The rifle left behind at the scene had a scope attached to it in a makeshift matter using electrical tape. Routh’s lawyers want their own experts to testify how well or whether it would have worked if fired at Trump that day.

Prosecutors say there’s no question that the gun worked. An FBI weapons expert test-fired the rifle when it was seized and processed as evidence. But they say the question of how well it worked is not relevant. More importantly, they say, is Routh’s alleged intent to attempt to kill then-Presidential candidate Donald Trump. If there was poor planning, problems with the gun, or other things that prevented the attack from happening, they say those details can’t be used as a defense.

Routh’s lawyers say if they aren’t granted access to the gun, they’d like all expert testimony about it excluded at trial. These are issues Judge Cannon will consider at Tuesday’s hearing.

Along with the attempted assassination of a presidential candidate, Routh is also charged with four other counts including federal weapons violations. Prosecutors have recently released some new details that they want to introduce at the trial. Those include messages recovered from Routh’s phone showing that he attempted to buy a 50-caliber rifle and a rocket launcher. That’s further evidence, they claim, of his intent. The defense hasn’t responded yet to the new information contained in court filings.

Routh’s trial is set to begin in September. The judge in this case, Aileen Cannon, also presided over Trump’s classified documents trial brought by Special Counsel Jack Smith. Cannon, who was appointed to the federal bench by Trump in his first term, ultimately dismissed the case that accused Trump of mishandling classified and top-secret documents at his Mar-a-Lago estate in Florida.

Takeaways about a whistleblower report about DOGE at NLRB : NPR

0

When a team of advisers from President Trump’s Department of Government Efficiency initiative arrived at the headquarters of the National Labor Relations Board, IT employees at the small, independent agency quickly became worried, according to a whistleblower declaration filed with Congress and shared with NPR.

The NLRB investigates and adjudicates complaints about unfair labor practices. Its databases store reams of potentially sensitive data, from confidential information about employees who want to form unions to proprietary business information.

The DOGE employees, who are effectively led by White House adviser and billionaire tech CEO Elon Musk, appeared to set their sights on accessing the NLRB’s internal systems, removing sensitive data and covering their tracks.

“I can’t attest to what their end goal was or what they’re doing with the data,” said the whistleblower, Daniel Berulis, in an interview with NPR. “But I can tell you that the bits of the puzzle that I can quantify are scary. … This is a very bad picture we’re looking at.”

Tim Bearese, the NLRB’s acting press secretary, denied that the agency granted DOGE access to its systems and said DOGE had not requested access to the agency’s systems. Bearese said the agency conducted an investigation after Berulis raised his concerns but “determined that no breach of agency systems occurred.”

Notwithstanding the NLRB’s denial, the whistleblower’s disclosure to Congress and other federal overseers provides evidence of DOGE’s access and activities. NPR’s reporting across the federal government also makes it clear that DOGE’s access to data is a widespread concern.

A representative of DOGE did not respond to NPR’s requests for comment.

Here are five takeaways from NPR’s reporting:

DOGE appeared to ignore standard security practices

Berulis says he was told by colleagues that DOGE employees demanded the highest level of access, what are called “tenant owner level” accounts inside the independent agency’s computer systems. Those offer essentially unrestricted permission to read, copy and alter data, according to Berulis’ disclosure to Congress.

When an IT staffer suggested a streamlined process to activate those accounts in a way that would let their activities be tracked, in accordance with NLRB security policies, the IT staffers were told to stay out of DOGE’s way, the disclosure continues.

For cybersecurity professionals, a failure to log activity is a cardinal sin and contradicts best practices.

“That was a huge red flag,” said Berulis. “That’s something that you just don’t do. It violates every core concept of security and best practice.”

According to the disclosure, someone had disabled controls that would prevent insecure or unauthorized mobile devices from logging on to the system without the proper security settings. There was an interface exposed to the public internet, potentially allowing malicious actors access to their systems. Internal alerting and monitoring systems were found to be manually turned off. Multifactor authentication was disabled.

Daniel Berulis hopes that there might be further investigations into mishandling of sensitive data across the federal government.

Daniel Berulis hopes that there might be further investigations into mishandling of sensitive data across the federal government.

Grace Raver/NPR


hide caption

toggle caption

Grace Raver/NPR

Berulis tracked sensitive data leaving the agency’s NxGen case management system “nucleus,” inside the NLRB system. Then, he saw a large spike in outbound traffic leaving the network itself. That kind of spike is extremely unusual, he explained in the disclosure, because data almost never directly leaves from the NLRB’s databases.

“If he didn’t know the backstory, any [chief information security officer] worth his salt would look at network activity like this and assume it’s a nation-state attack from China or Russia,” said Jake Braun, a former White House cyber official.

In fact, in the minutes after DOGE accessed the NLRB’s systems, someone with an IP address in Russia started trying to log in, according to Berulis’ disclosure. Those attempts were blocked, but they were especially alarming. Whoever was attempting to log in was using one of the newly created DOGE accounts — and the person had the correct username and password, according to Berulis.

The NLRB’s data is extremely sensitive and has little to do with DOGE’s cost-cutting mission

DOGE’s intentions with regard to the NLRB data remain unclear. Many of the systems DOGE embedded itself in across the rest of the government have payment or employment data — information that DOGE could use to evaluate which grants and programs to halt and whom to fire.

But the NxGen case management system is very different.

It houses information about ongoing, contested labor cases, lists of union activists, internal case notes, personal information from Social Security numbers to home addresses, proprietary corporate data and more information that never gets published openly. Access to that data is protected by numerous federal laws, including the Privacy Act.

“There is nothing that I can see about what DOGE is doing that follows any of the standard procedures for how you do an audit that has integrity and that’s meaningful and will actually produce results that serve the normal auditing function, which is to look for fraud, waste and abuse,” said Sharon Block, the executive director of Harvard Law School’s Center for Labor and a Just Economy and a former NLRB board member.

Elon Musk’s businesses are the subject of NLRB investigations

There are multiple ongoing cases involving the NLRB and companies controlled by Musk. After a group of former SpaceX employees lodged a complaint with the NLRB, lawyers representing SpaceX, some of whom were recently hired into government jobs, filed suit against the NLRB. They argued that the agency’s structure is unconstitutional.

Trump and Musk, during an interview with Fox News’s Sean Hannity, said Musk would recuse himself from anything involving his companies. “I haven’t asked the president for anything ever,” Musk said. “I’m getting a sort of a daily proctology exam here. You know, it’s not like I’ll be getting away [with] something in the dead of night.” However, DOGE has been granted high-level access to a lot of data that could benefit Musk, and there has been no evidence of a firewall preventing misuse of that data.

The National Labor Relations Board (NLRB) seal hangs inside a hearing room at the headquarters in Washington, D.C., U.S., in 2019.

The National Labor Relations Board (NLRB) seal hangs inside a hearing room at the headquarters in Washington, D.C., U.S., in 2019.

Andrew Harrer/Bloomberg via Getty Images


hide caption

toggle caption

Andrew Harrer/Bloomberg via Getty Images

“It’s not that he’s a random person who’s getting information that a random person shouldn’t have access to,” said Harvard Law’s Block. “But if they really did get everything, then he has information about the cases the government is building against him,” she said.

“DOGE is, whether they admit it or not, headed by somebody who is the subject of active investigation and prosecution of cases. It is incredibly troubling,” she said.

DOGE has a pattern of seeking sensitive data and not protecting it 

In over a dozen lawsuits in federal courts around the United States, judges have demanded that DOGE explain why it needs such expansive access to sensitive data on Americans, from Social Security records to private medical records and tax information. But the Trump administration has been unable to give consistent and clear answers, largely dismissing cybersecurity and privacy concerns.

The Trump administration could be trying to codify DOGE’s practices into how the government shares information, said Kel McClanahan, the executive director of nonprofit public interest law firm National Security Counselors, who is representing federal employees in a lawsuit concerning the Office of Personnel Management’s use of a private email server.

Weeks after DOGE staffers descended on federal buildings across Washington, Trump issued an executive order urging increased data sharing “by eliminating information silos” in what’s seen by experts like McClanahan as an attempt to give DOGE engineers further top cover in accessing and amalgamating sensitive federal data, despite laws concerning privacy and cybersecurity.

“The entire reason we have a Privacy Act is that Congress realized 50 years ago that the federal government was just overflowing with information about normal everyday people and needed some guardrails in place,” McClanahan told NPR. “The information silos are there for a reason,” he continued.

Labor experts fear the release of this data could hurt organized labor

Access to the NxGen data would make it easier for companies to fire employees for union organizing or keep blacklists of organizers — illegal activities under federal labor laws enforced by the NLRB. But “people get fired in this country all the time for the lawful act of trying to organize a union,” said Block.

Having a list of key organizers and potential members of a union would make that easier, as would having a copy of the opposing counsel’s notes as companies prepare for legal challenges, she continued.

It’s not just employees who might suffer if this data got out. Companies also sometimes provide detailed statements on internal business planning and corporate structure in the midst of unfair-labor-practice complaint proceedings. If a company was attempting to fire someone who it alleged had disclosed trade secrets and was fighting an unfair-labor-practice complaint based around that decision, those trade secrets might come up in the NLRB’s investigation. That information would be valuable to competitors, regulators and others.

Overall, the potential exposure of the NLRB’s data could have serious implications.

“I think it is very concerning,” said University of California, Berkeley, labor scholar Harley Shaiken. “It could result in damage to individual workers, to union-organizing campaigns and to unions themselves,” he said.

NPR’s Stephen Fowler contributed reporting. NPR’s Brett Neely edited this story. 

Have information or evidence to share about DOGE’s access to data inside the federal government? Reach out to the author, Jenna McLaughlin, through encrypted communications on Signal at jennamclaughlin.54. Stephen Fowler is available on Signal at stphnfwlr.25. Please use a nonwork device.
CDC’s vaccine advisory meeting set to start after delays : Shots

0

An advisory committee of the Center for Disease Control and Prevention is set to meet Tuesday to discuss vaccines for RSV, COVID and others.

Jeff Amy/AP


hide caption

toggle caption

Jeff Amy/AP

For the first time since Robert F. Kennedy Jr. took charge of the Department of Health and Human Services, vaccine advisers to the Centers for Disease Control and Prevention are meeting publicly to discuss the nation’s vaccine policies.

A meeting of the CDC’s advisory committee on immunization practices was initially scheduled for February but was postponed, raising concerns among some scientists and those working in public health about political interference in vaccine policy. The two-day meeting starts Tuesday morning.

The committee’s advice shapes access to and insurance coverage for vaccines.

“I’m reassured and very glad to see that it’s happening,” says Claire Hannan, executive director of the Association of Immunization Managers. “It’s important to have this ongoing review of data and science, looking at the evidence that goes into the vaccine schedule in an open forum.”

The advisory committee typically holds public meetings three times a year, which are live streamed online.

During this week’s meeting, the committee’s independent advisors will hear from CDC staff on a range of vaccines, including HPV, COVID and flu, and vote on recommendations for some of them such as RSV and the tropical mosquito-borne viral disease chikungunya.

The current agenda is similar to the proposed agenda for February, though it omits a vote on influenza vaccines that was on that agenda.

When asked about the change, HHS spokesperson Emily Hilliard responded on behalf of CDC: “ACIP agenda items are always subject to change depending on what the working groups have ready for consideration.” She further clarified: “This was not the annual vote for the routine use of the influenza vaccine for the upcoming season.”

The advisors are independent experts who volunteer to serve on the committee. Dorit Reiss, a law professor at UC San Francisco, says she expects them to remain independent and hold thoughtful, rigorous discussions as they usually do.

But she’s concerned about the effects of political interference on CDC staff who help run these meetings, who “are in a much more vulnerable position after extensive layoffs,” Reiss says.

There have been deep cuts to CDC staff since President Trump took office, including some officials who would have participated or spoken in this week’s meeting.

It’s had a chilling effect on those who are left.

“I’ll be looking to see if they change the process in any way,” Reiss says. For example she says she’ll be watching for changes in how conflicts of interest are handled – a topic Kennedy has raised repeatedly – or whether they put time limits on discussions among committee members, Reiss says.

Signs of political interference may be subtle, says Katelyn Jetelina, an epidemiologist and data scientist who writes the newsletter “Your Local Epidemiologist.” What it may take, she says, is “for those of us that have listened to hundreds of ACIP meetings to report back whether it is just business as usual or there’s some sketch things beneath the surface.”

Vaccine advocates are concerned over potential shifts in policy and official stances that may reduce confidence in vaccines.

“What I don’t want to see go away is a very strong endorsement of the use of vaccines as preventive medicine,” says Dr. Anthony Fiore, a former CDC official who worked closely with the vaccine advisory committee before retiring from the agency in 2021.

He’s concerned because Kennedy has cast doubt on vaccine safety and canceled funding for research into vaccine hesitancy.

“Up to this point, every HHS director and every CDC director has been very enthusiastic about vaccines as they save money and they’re an excellent preventive tool,” Fiore says. But if public confidence in vaccines gets undermined, vaccination levels could drop below the levels needed to reduce transmission and protect the population from disease, he says.

Bipartisan senators rebuke White House move to end legal aid for unaccompanied minors : NPR

0

Asylum seekers from Honduras walk towards a U.S. Border Patrol checkpoint after crossing the Rio Grande from Mexico in 2021 near Mission, Texas.

John Moore/Getty Images


hide caption

toggle caption

John Moore/Getty Images

Two senators are mounting a rare bipartisan attack against the Trump administration’s approach to due process for migrants.

Sen. Lisa Murkowsi, R-Alaska, joined Sen. Jon Ossoff, D-Ga., in a letter criticizing the end of a federal contract that provides legal representation to 26,000 children who are in the U.S. without a parent or guardian.

The decision to end the contract in late March “puts children directly at risk of trafficking and exploitation, and harms any hope of a fair legal process for thousands of vulnerable children,” they wrote to Health and Human Services Secretary Robert F. Kennedy Jr. on Tuesday.

The letter, which was obtained by NPR, marks rare bipartisan condemnation from Capitol Hill of the administration’s immigration policy; so far, Democrats have sent most of the letters raising questions or concerns.

The administration last month ended a contract with the Acacia Center for Justice, which provided legal services to unaccompanied migrant children under the age of 18, including in-court representation and clinics.

“Terminating legal representation for these children means that toddlers will now face a courtroom and judge with no adult to advocate on their behalf,” Ossoff and Murkowski wrote. “Children will be asked to make decisions about their legal rights well beyond their comprehension, with life-altering consequences.”

The Office of Refugee Resettlement is part of HHS and manages programs related to unaccompanied migrant children. HHS did not respond to a request for comment. In court filings, it has argued that federal agencies have discretion on whether to keep funding such legal services.

Dispute over 2008 trafficking law

Ossoff and Murkowski raised concerns that ending the legal funding under the contract would violate the Trafficking Victims Protection Reauthorization Act of 2008.

The act requires “HHS to ensure, to the greatest extent practicable, that all unaccompanied children have counsel to represent them in legal proceedings,” Ossoff and Murkowski wrote.

Their letter follows a similar appeal from House members last month.

Several subcontractor groups that received funding from Acacia sued over the contract termination, also arguing the stop in funding violated the 2008 law.

But lawyers representing HHS have argued that the 2008 law leaves much in the hands of the agency; it “does not create an enforceable right to government-funded representation, let alone compel the agency to maintain any particular scope of services or contractual relationship.”

A federal judge issued a temporary restraining order in the groups’ favor in early April, and ordered HHS to restore funding at least until the end of the month.

In response, the administration agreed to extend the contract for six more months to wind down programmatic work and find new representation for the children.

But it’s unclear what happens after that.

“After the six-month extension, there are a lot of open questions about what protections these vulnerable kids will have,” Shaina Aber, executive director of the Acacia Center for Justice, said in an interview.

“It is incredibly important that children are provided with an understanding of their rights to be safe and free from harm and to report rights violations to independent legal services providers who can advocate on behalf of children.”

The Justice Department separately issued an order to stop funding work across several other Acacia programs in immigration court, including assistance for the guardians of unaccompanied children.

Veteran diplomats react to the Trump administration gutting the lead U.S. aid agency

0

Trump administration reforms at the State Department are shrinking the United States’ diplomatic footprint globally.

Medicaid cuts could slash fentanyl addiction treatment : NPR

0

A woman reached for a dose of methadone at the Behavioral Health Network opioid treatment clinic.

Boston Globe via Getty Images/Boston Globe


hide caption

toggle caption

Boston Globe via Getty Images/Boston Globe

As Republican lawmakers search for deep spending cuts, a growing number of critics fear a roll-back of Medicaid dollars spent helping Americans slammed by the street fentanyl crisis.

A report released Monday by Democrats on the Congressional Joint Economic Committee warned medical treatment for more than a million people in the U.S. now receiving medical treatment for opioid addiction, including fentanyl, could be affected.

“President Trump and Congressional Republicans have proposed gutting Medicaid— in order to pay for tax breaks for corporate special interests and billionaires — which would jeopardize addiction care just as our country is finally starting to see progress in addressing the fentanyl crisis,” said Sen. Maggie Hassan, a Democrat from New Hampshire, in a statement.

Over the last decade, as more states expanded Medicaid coverage under provisions of the Affordable Care Act, the program emerged as the leading source of insurance coverage for high quality addiction treatment in the U.S.

A study released in February by the Brookings Institution, a centrist think-tank that focuses extensively on drug policy issues, found nearly 90 percent of medical treatment for opioid and fentanyl addiction in the U.S. is paid for at least in part through Medicaid.

Most drug policy experts say that funding helped reduce drug overdose deaths, which plunged 26.6 percent nationwide from June 2023 to October 2024, according to the latest provisional data from the Centers for Disease Control and Prevention.

But the Affordable Care Act remains a target for many GOP lawmakers, who view the Obama-era program with suspicion. While it’s not yet clear how Republican budget proposals will impact Medicaid and its role in drug treatment, House GOP leaders have floated ideas that include slashing as much as $2.3 trillion from the program over the next decade.

House Budget Committee Chairman Jodey Arrington, R-Texas, right, and Speaker of the House Mike Johnson, R-La., have both called for major cuts to Medicaid which grew into a major source of addiction treatment funding under the Affordable Care Act.

House Budget Committee Chairman Jodey Arrington, R-Texas, right, and Speaker of the House Mike Johnson, R-La., have both called for major cuts to Medicaid which grew into a major source of addiction treatment funding under the Affordable Care Act.

Tom Williams/CQ-Roll Call, Inc via Getty Imag/CQ-Roll Call, Inc.


hide caption

toggle caption

Tom Williams/CQ-Roll Call, Inc via Getty Imag/CQ-Roll Call, Inc.

Speaking over the weekend with Fox News, House Speaker Mike Johnson suggested young men, who are highly vulnerable to drug addiction and account for the vast majority of U.S. overdose deaths, should not qualify for Medicaid insurance.

“We have to eliminate people for example on Medicaid who are not eligible to be there, able-bodied workers, for example, young men, who should never be on the program at all,” Johnson said.

Research shows men are two to three times more likely to die from drug deaths, compared with women; and fentanyl is now a leading cause of death for men under the age of fifty.

A growing number of addiction researchers, doctors and people who survived drug addiction have raised alarm deep Medicaid cuts could derail the national recovery from the fentanyl-overdose epidemic.

“It’s very hard to look at the budget framework created by Republicans and imagine a scenario other than Medicaid being cut severely,” said Stanford University’s Keith Humphreys speaking with NPR last month. “It’s a frightening prospect. That will be extremely painful for families facing addiction.”

In a statement, Dr. Brian Hurley, head of the American Society of Addiction Medicine, urged lawmakers to protect Medicaid expansion for Americans facing addiction.

“It not only helps states pay for evidence-based addiction treatment…but it also undermines the drug cartels’ business model by reducing demand for illicit opioids,” Hurley said.

The Brookings Institution report concluded that a major rollback of Medicaid expansion could drastically reduce addiction care nationwide.

“Since Medicaid payments for treatment of OUD [opioid use disorder] dwarfs all other public sources of funding for OUD care, significant reductions would substantially reduce the nation’s economic commitment to addressing the opioid epidemic,” the Brookings report found.

El Salvador’s Bukele says he’s not inclined to return Abrego Garcia : NPR

0

President Trump meets with President Nayib Bukele of El Salvador in the Oval Office on April 14, 2025.

Win McNamee/Getty Images


hide caption

toggle caption

Win McNamee/Getty Images

El Salvador’s President Nayib Bukele said on Monday that he was not inclined to return Kilmar Armando Abrego Garcia to the United States.

Abrego Garcia, a Salvadoran citizen who had lived in Maryland for about 15 years, was deported to El Salvador despite being granted protections by an U.S. immigration judge. He is in custody in Bukele’s mega prison known as CECOT. The Supreme Court ordered the Trump administration to facilitate his return.

During Bukele’s Oval Office visit on Monday, Trump and his team said it was up to the Salvadoran government to decide whether to return him. Bukele said he would not do that.

“The question is preposterous: how can I smuggle a terrorist into the United States?” Bukele said.

White House deputy chief of staff Stephen Miller speaks during an Oval Office meeting with President Nayib Bukele of El Salvador as Vice President Vance, Secretary of State Marco Rubio and Attorney General Pam Bondi look on.

White House deputy chief of staff Stephen Miller speaks during an Oval Office meeting with President Nayib Bukele of El Salvador as Vice President Vance, Secretary of State Marco Rubio and Attorney General Pam Bondi look on.

Win McNamee/Getty Images


hide caption

toggle caption

Win McNamee/Getty Images

Secretary of State Marco Rubio and White House deputy chief of staff Stephen Miller said the matter was up to Bukele. “He’s a citizen of El Salvador, so it’s very arrogant even for American media to suggest that we would even tell El Salvador, how to handle their own citizens,” Miller said.

Rubio emphasized that no court in the United States had the right to conduct foreign policy.

Attorney General Pam Bondi said that Abrego Garcia was not in the United States legally and downplayed the issue with his deportation as a “paperwork” issue. “That’s up to El Salvador if they want to return him. That’s not up to us,” Bondi said in the Oval Office meeting.

She said the only obligation the U.S. had to “facilitate” his return was to provide a plane.